See your organisation from the outside
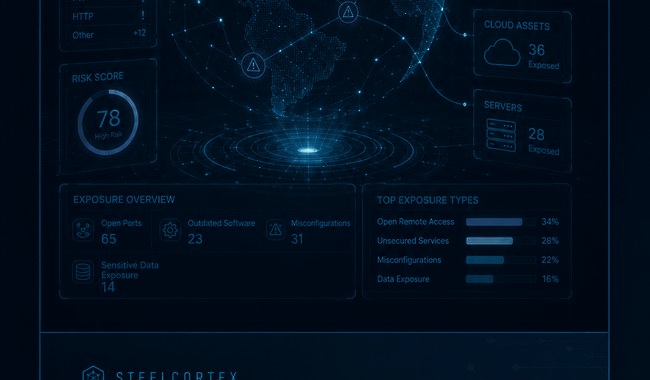
External exposure changes as domains, cloud services, applications and suppliers are added or retired. Assets can remain visible long after internal teams believe they are no longer in use. SteelCortex helps establish what is publicly reachable, who owns it and which exposures deserve attention first.
Areas reviewed
- Domains, subdomains and related public infrastructure.
- Internet-facing ports, services and administration interfaces.
- TLS certificates, DNS and email-security configuration.
- Public APIs, cloud endpoints and storage exposure.
- Technology fingerprints and outdated public services.
- Unknown, forgotten or third-party-hosted assets associated with the organisation.
Prioritising exposure
An exposed service is not automatically a critical incident. SteelCortex considers the sensitivity of the asset, authentication requirements, known vulnerabilities, exploitability, business purpose and whether compensating controls reduce the realistic risk.
What the report provides
Outputs can include an external asset inventory, confirmed exposure evidence, ownership questions, priority findings and a remediation plan. The report separates quick wins—such as closing an unused service—from longer-term work such as redesigning remote access or improving asset lifecycle management.
Continuous improvement
Attack-surface reviews are most effective when repeated. Monitoring can identify new public assets or changes over time so the organisation is not relying on a one-off snapshot of its external footprint.