Turn fragmented evidence into an understandable case
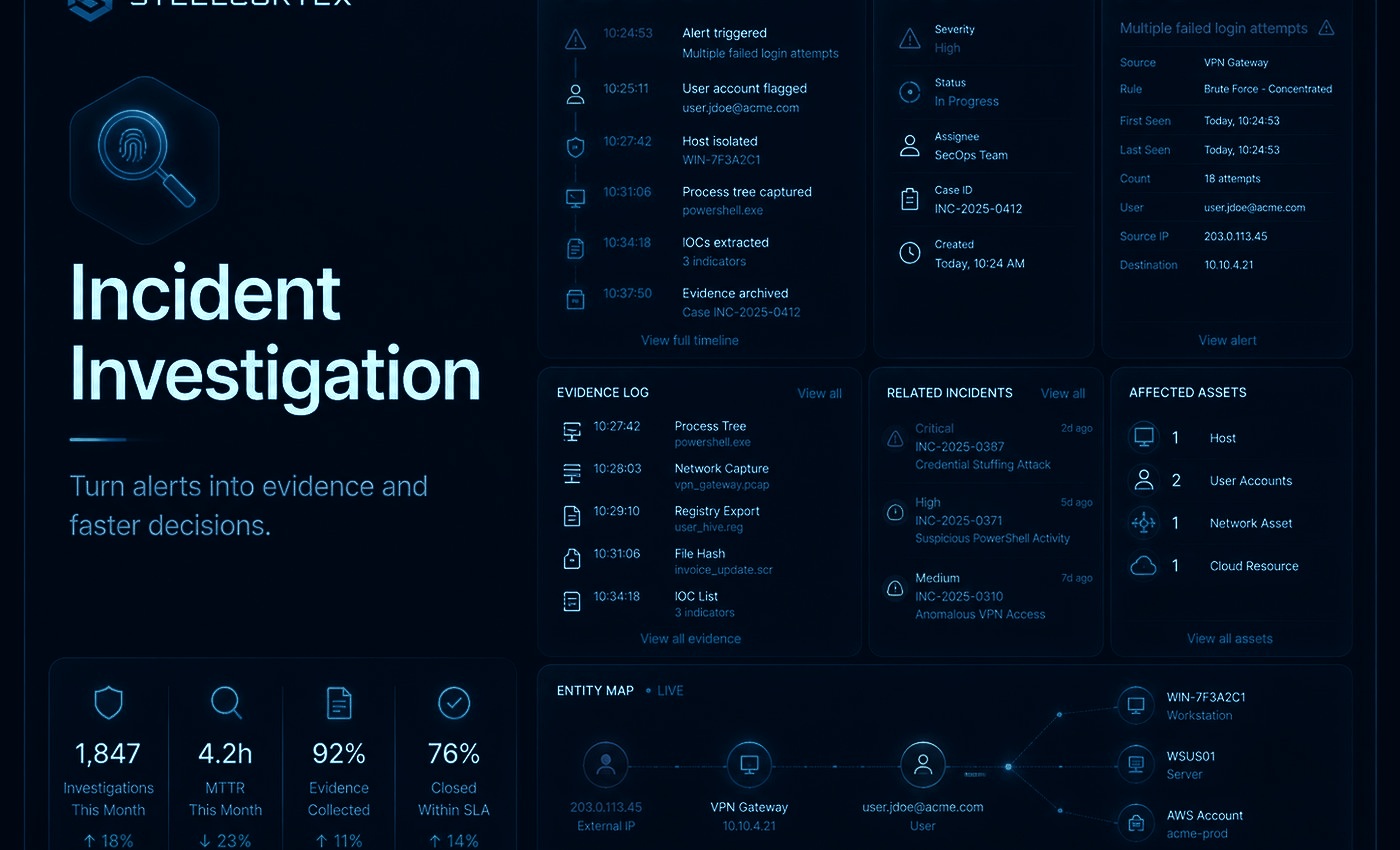
Incident investigations often begin with incomplete information spread across email, identity, endpoint, cloud and network systems. The SteelCortex Investigation Centre is designed to organise those fragments into a structured case so teams can understand the sequence of events and make defensible response decisions.
Core investigation capabilities
- Case creation and incident ownership.
- Evidence collection and source tracking.
- Chronological event timelines.
- Identity, asset and alert correlation.
- Attack-path and root-cause analysis.
- Containment and remediation records.
- Investigation notes, uncertainty and analyst judgement.
- Case summary and reporting hand-off.
Evidence before assumption
Security incidents can generate strong suspicions before the evidence is complete. SteelCortex is intended to distinguish confirmed facts, likely interpretations and unresolved questions so response teams do not treat an assumption as proof.
Preserve the story of the incident
A useful investigation record should show not only the final conclusion but how that conclusion was reached. Timelines, evidence references and analyst notes help technical teams, management and external specialists understand what was observed and why particular actions were taken.
Connect investigation to remediation
Closing the immediate incident is only part of the job. Findings should flow into vulnerability, identity, configuration or process improvements so the weakness that enabled the incident is less likely to recur.